Strategy & Governance
Program design, ownership, maturity, roadmaps, risk decisions, and operating cadence.
The Product Security Knowledge Base turns years of practical experience into reusable guidance for engineers, architects, security leaders, and teams building modern software.
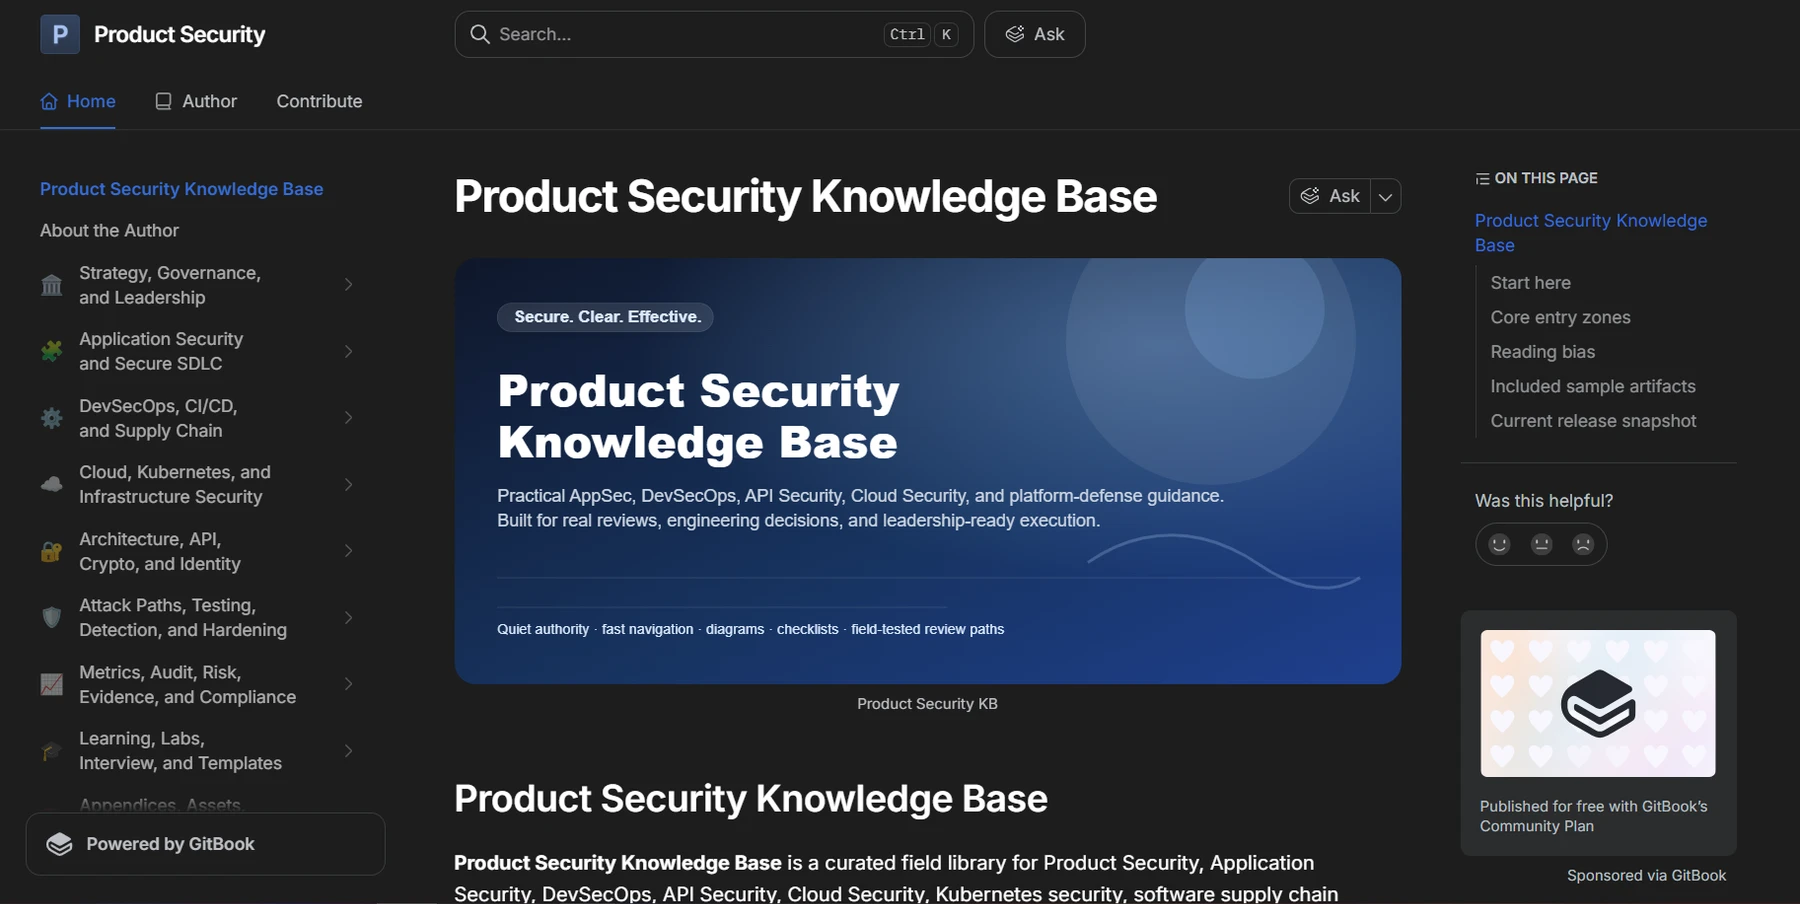
The library spans the operating model around Product Security, not only individual vulnerability classes or tools.
Program design, ownership, maturity, roadmaps, risk decisions, and operating cadence.
Requirements, secure delivery, testing, remediation, coverage, and engineering workflows.
Trust boundaries, attack paths, product design decisions, APIs, identity, and authorization.
Pipeline trust, runners, secrets, security gates, artifacts, release controls, and automation.
AWS, IAM, workloads, containers, RBAC, networking, policies, logging, and platform risk.
Dependencies, SBOM, build integrity, signing, provenance, registries, and release trust.
KPI/KRI design, engineering capacity, security debt, reporting, prioritization, and budgets.
Vulnerability management, PSIRT thinking, evidence, technical validation, and feedback loops.
The project is designed to make Product Security easier to understand, implement, validate, and connect to business impact.
It also creates public accountability: prospective clients and practitioners can review the underlying thinking before deciding whether the approach fits their environment.
Documentation-first navigation for readers who want a structured handbook and reference system.
Open docs.product-security.expert ↗Main knowledge projectThe primary public knowledge-base site with the broader project structure and supporting material.
Open product-security.expert ↗The Knowledge Base is one part of a broader proof-in-public ecosystem across Bulwark Advisory, DEV Community, and GitHub.