Product Security Baseline Sprint
From $3,5005–7 business days
A compact first engagement for a product team that needs clarity quickly.
- Product and architecture baseline
- Top risks and control gaps
- Prioritized 30/60/90-day plan
Senior Product Security expertise for startups, scale-ups, and growing software companies — without the overhead of building a large in-house security function first.
A practical fit for teams that are shipping fast, selling to larger customers, preparing for diligence, or reaching the point where ad-hoc security stops scaling.
A compact first engagement for a product team that needs clarity quickly.
For teams moving up-market, launching a major product, or facing customer security scrutiny.
Ongoing senior security direction when a full-time Product Security leader is not yet the right hire.
Focused engagements that can stand alone or combine into one Product Security program.
Know where your Product Security program stands — and what to improve first.
Find architectural risk before it becomes a production vulnerability.
Turn security checks into scalable engineering controls — not pipeline friction.
Review cloud identities, workloads, clusters, infrastructure, and delivery paths.
Protect dependencies, builds, artifacts, provenance, and release trust.
Senior Product Security direction without waiting to build a full internal function.
For teams that do not need a heavyweight ASPM, SIEM, or custom platform, lightweight automation can normalize scanner exports and engineering data into practical Product Security views.
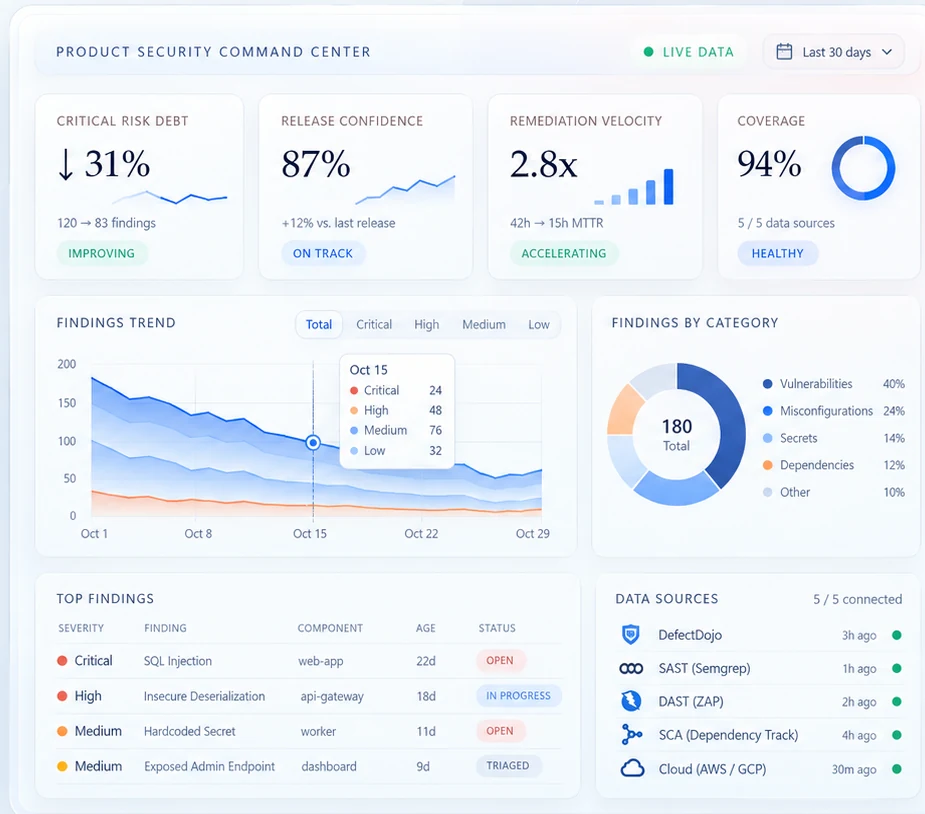
Automated tooling is useful for breadth. The value is deciding what matters to the product, where attack paths exist, what engineering should fix first, and what leadership needs to know.
Senior Product Security involvement from discovery through final decisions.
Controls designed to fit how a lean software team actually ships.
Start with the smallest engagement that can answer the real decision.
Technical findings translated into priorities, tradeoffs, and measurable progress.
Engagements are designed for distributed product and engineering teams across time zones. Geography changes logistics — not the quality of the security work.
Typical fit: North America, Europe, the UK, Middle East, Africa, Asia-Pacific, Latin America, and other English-speaking or internationally operated software teams.
Discuss location and scopeBulwark Advisory publishes practical material openly: a Product Security knowledge base, engineering resources, company articles, and community updates.
A free, continuously developed body of Product Security practices, operating models, Secure SDLC guidance, cloud, Kubernetes, supply-chain, metrics, and leadership material.
Open knowledge base ↗DocumentationA documentation-first view of the same Product Security knowledge base for readers who prefer a structured handbook and reference format.
Open GitBook ↗Open EngineeringCompany-maintained repositories for practical checklists, scripts, security engineering utilities, reusable templates, and Product Security program material.
Explore GitHub ↗Company WritingProduct Security, AppSec, DevSecOps, security engineering, operating-model, and delivery lessons published under the company name.
Read articles ↗The advisory practice is supported by open knowledge, reusable engineering material, field guides, research, and long-form technical writing.
A free knowledge project consolidating years of practical Product Security experience across strategy, Secure SDLC, architecture, AppSec, DevSecOps, cloud, Kubernetes, supply chain, metrics, and leadership.
Explore the knowledge baseCompany GitHubReusable checklists, scripts, utilities, templates, and Product Security program material maintained for practical use.
Open Bulwark GitHubCompany ArticlesField notes and long-form writing on Product Security, AppSec, DevSecOps, engineering systems, and security operating models.
Read company articlesGitBookA structured documentation view of the Product Security Knowledge Base for handbook-style navigation and reference.
Open GitBook docsPublished BookA 156-page technical guide covering Kubernetes attack surface, security controls, attack scenarios, and CKS-oriented practice.
View publicationEngineering NotesReusable security notes and practical references across AppSec, pipelines, cloud, containers, and delivery security.
Open repositoryField GuideA practical guide to trust boundaries, runner risk, secrets exposure, deployment governance, and audit readiness.
View resourcesOpen SourceKubernetes security checks and hardening-oriented tooling built around practical cluster review.
Open projectComing Soon · 2026Defense-oriented Product Security for EV charging platforms and software-defined vehicle ecosystems — cloud, APIs, identity, CI/CD, firmware, OTA, telemetry, device trust, and recovery.
Preview casebookCloud Attack LabA hands-on lab showing how SSRF can expose EC2 metadata credentials and turn application-layer weakness into cloud IAM risk.
Read technical labWe can define a narrow first scope, create useful evidence quickly, and expand only if the problem justifies it.